Single Sign-On
Single Sign-On with Okta
Let your team members log in to AssetNode using their Okta credentials.
คู่มือการตั้งค่า (5 ขั้นตอน)
1
Log in to your Okta account
Navigate to your Okta admin dashboard.
2
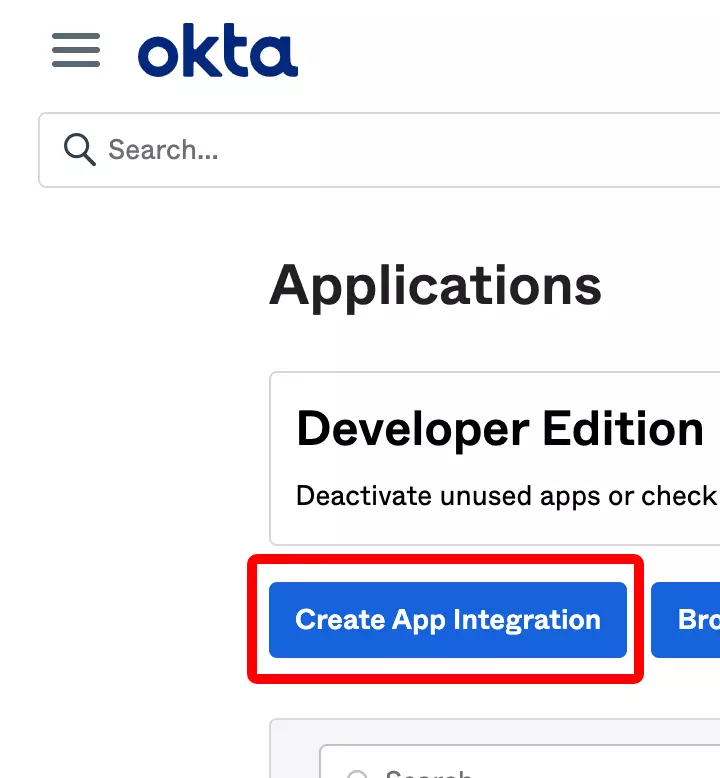
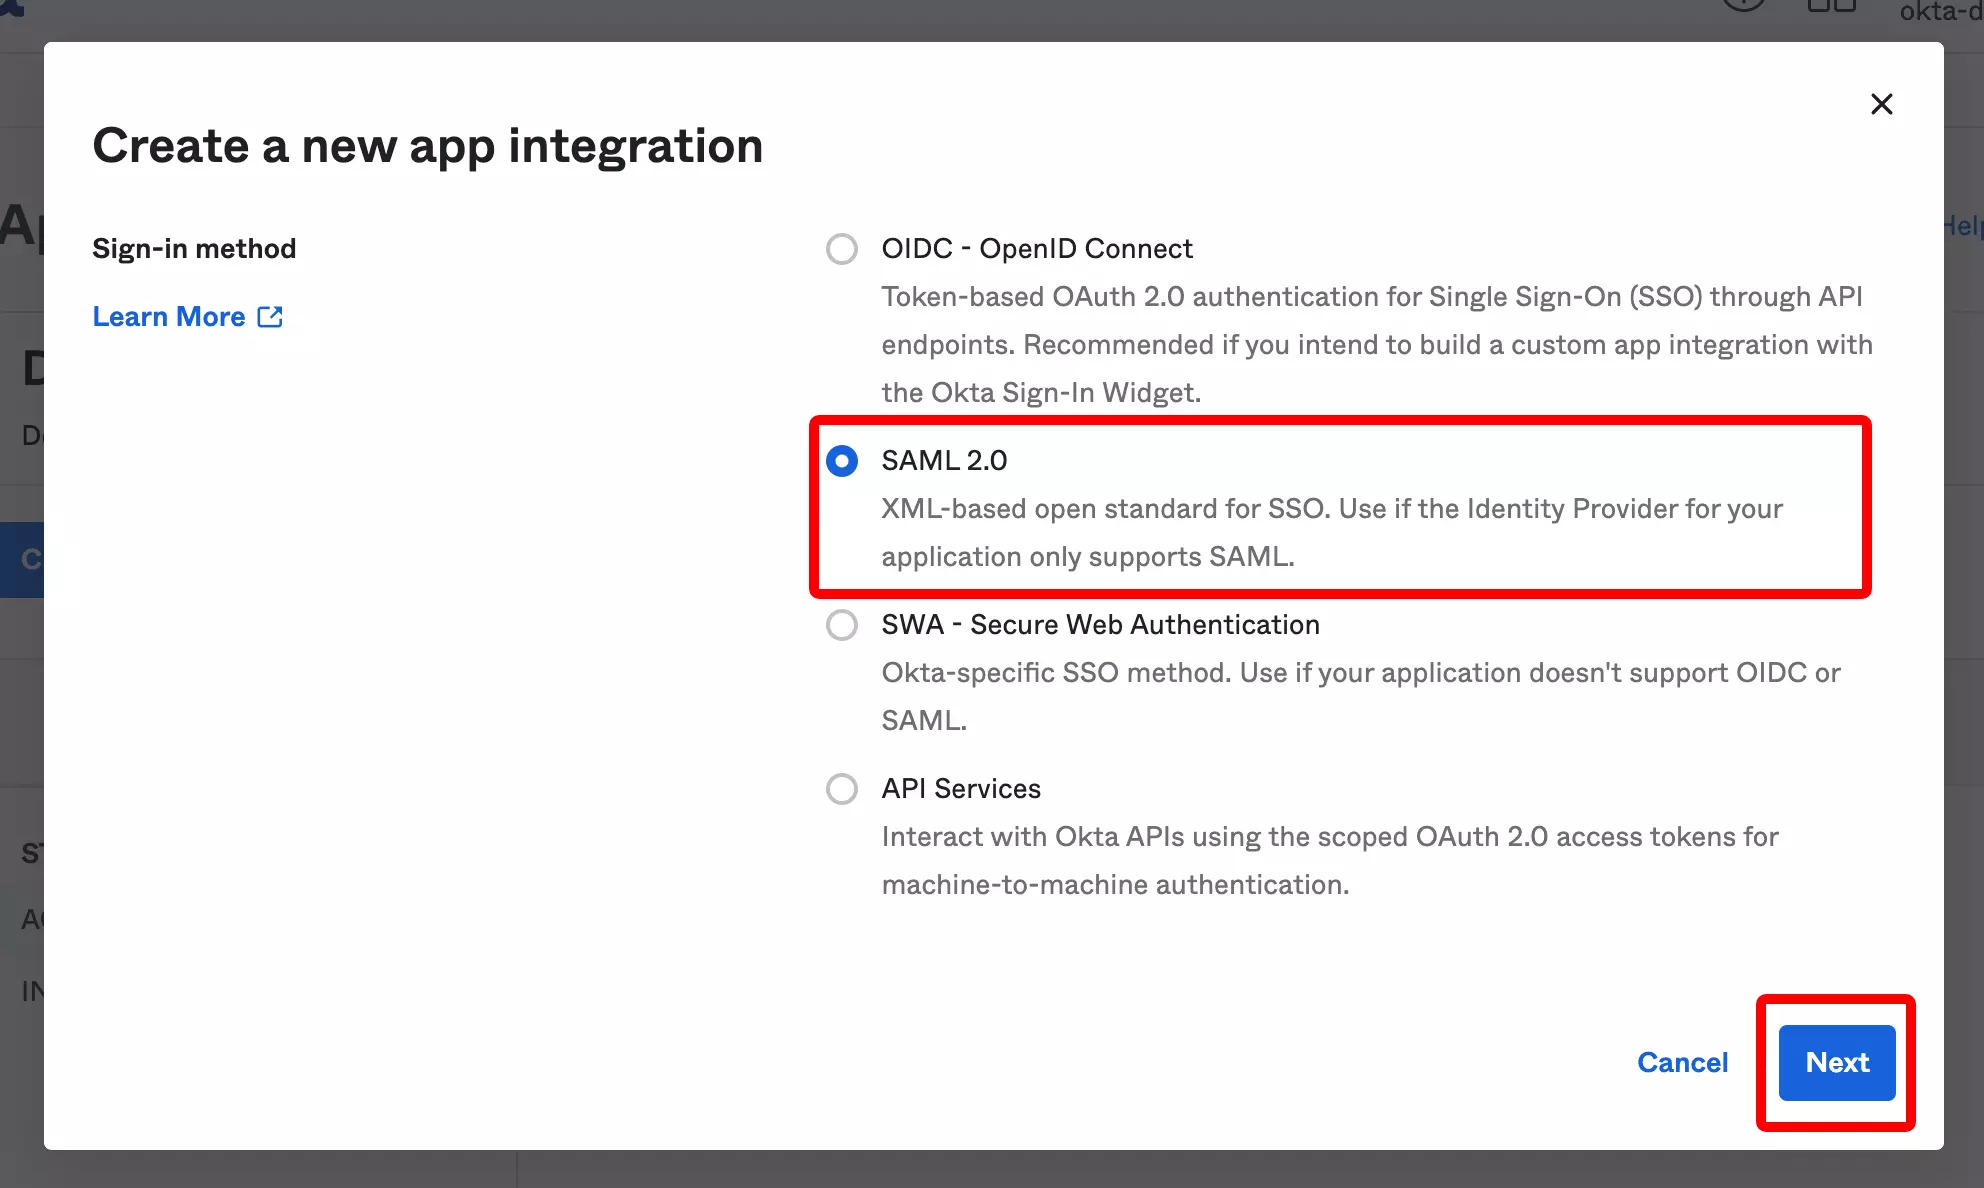
Create a new SAML application
Go to Applications → Create App Integration → Select "SAML 2.0".
3
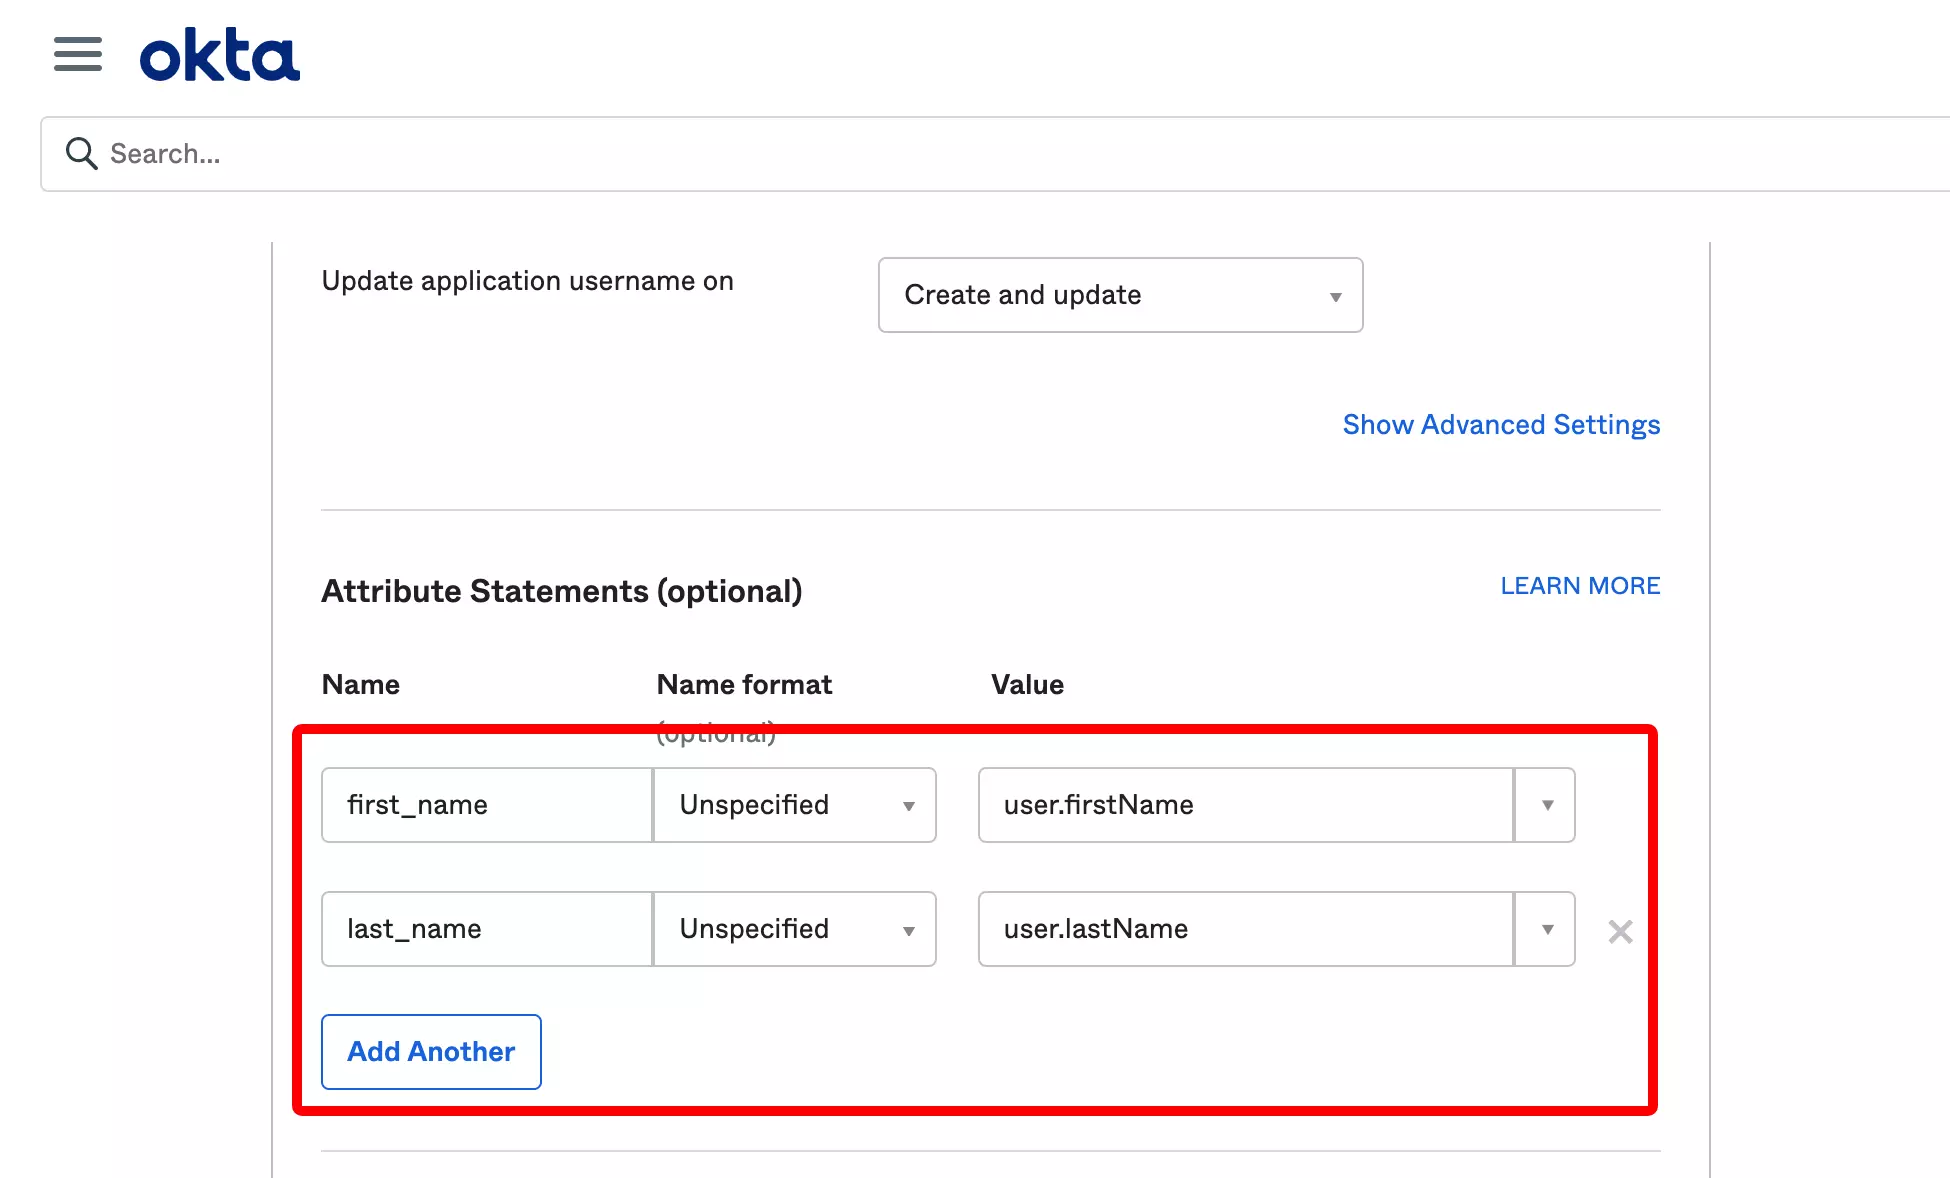
Configure SAML Settings
Set the SSO URL and Audience URI from AssetNode settings.
4
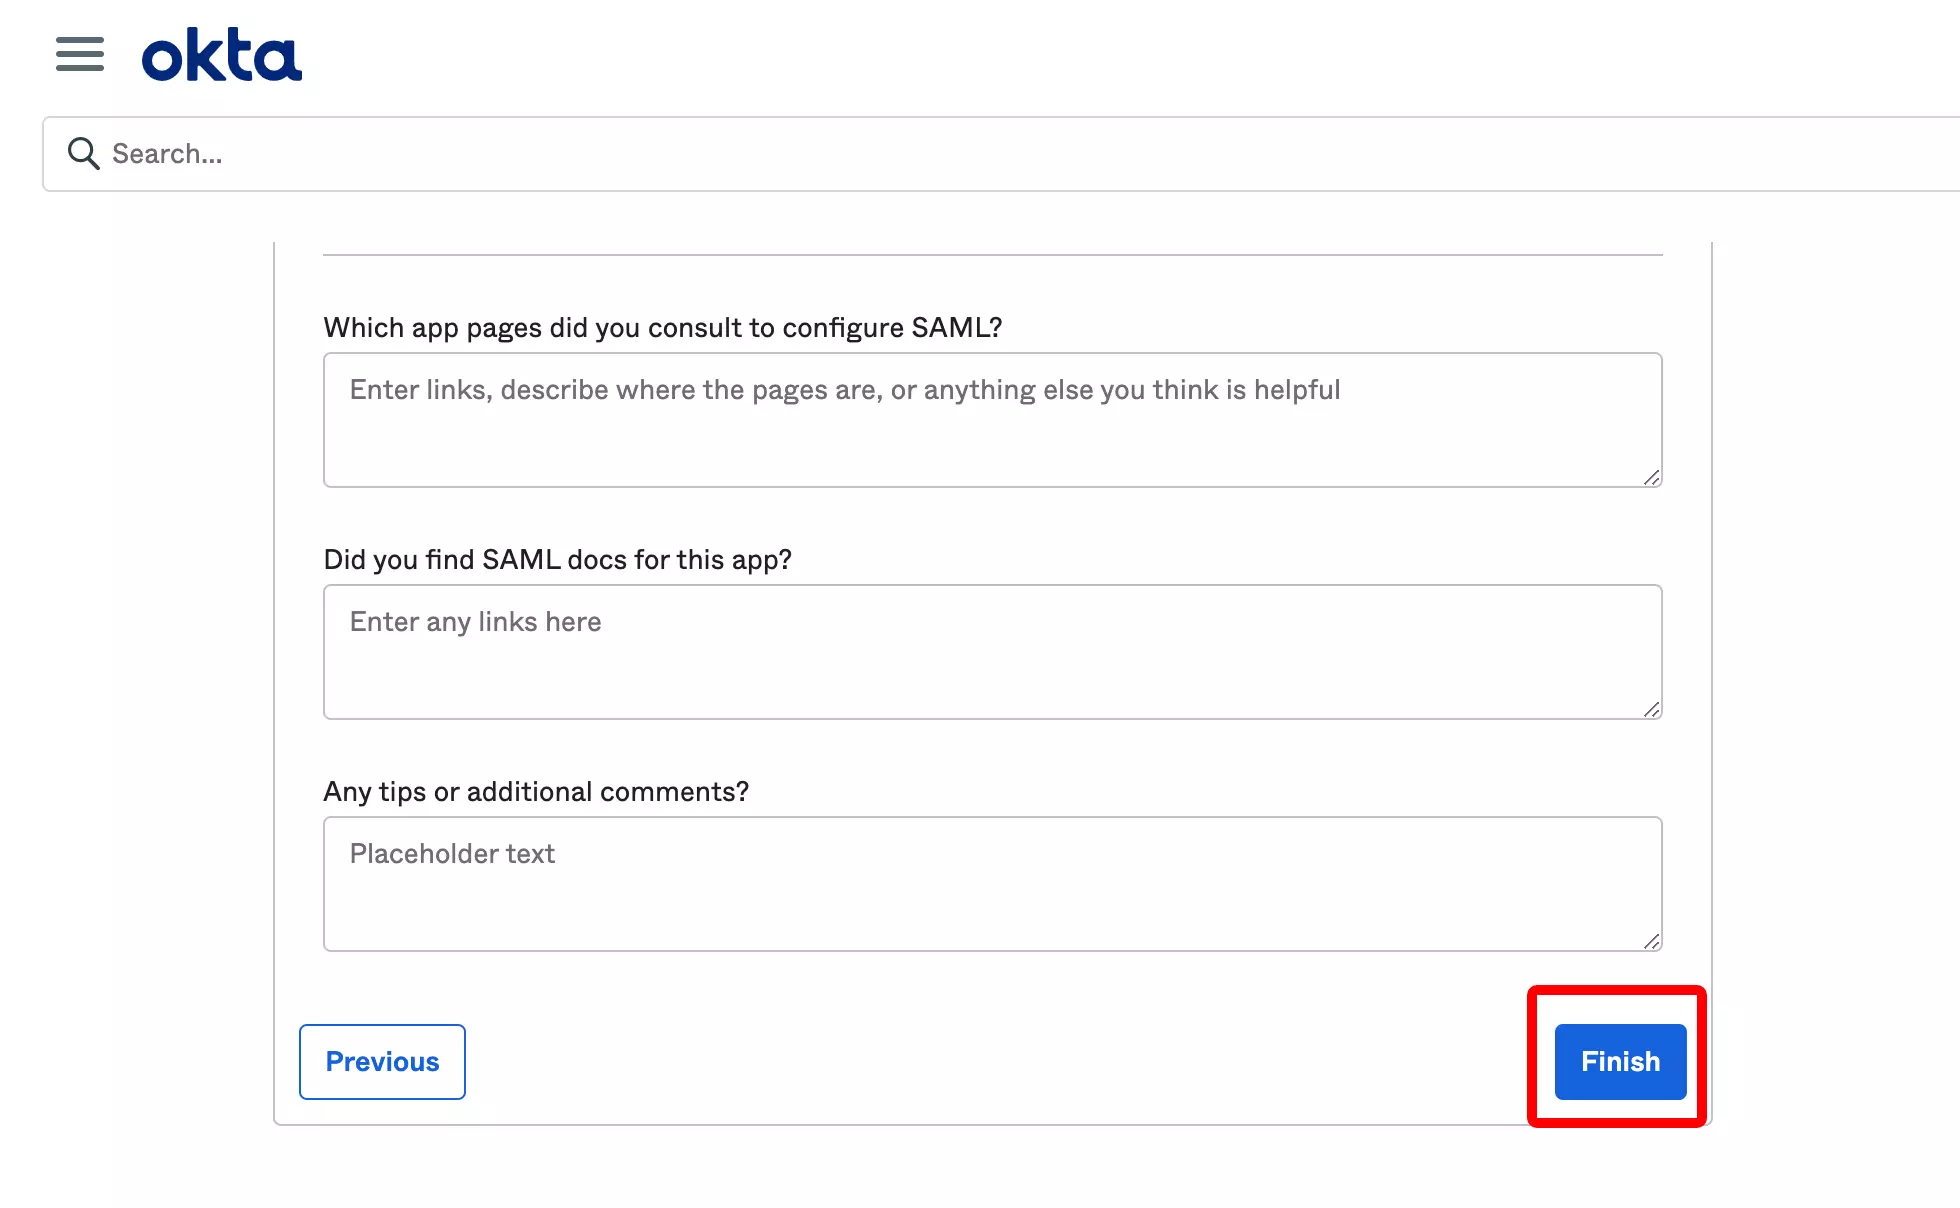
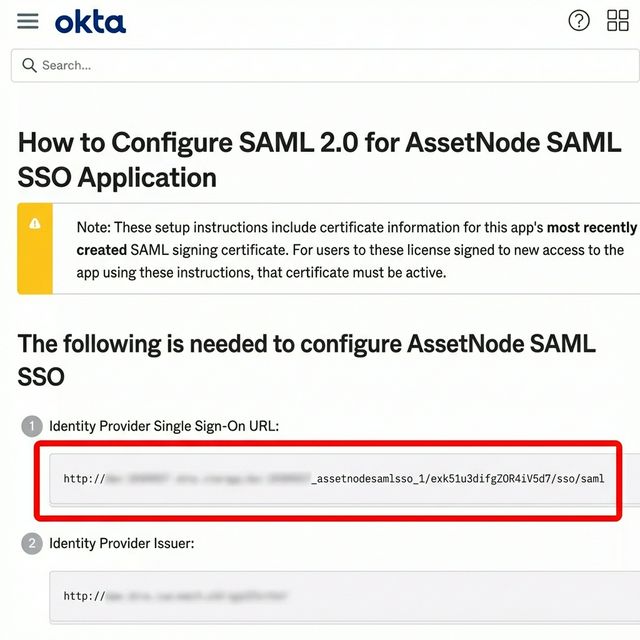
Copy IdP metadata
Copy SSO URL and download certificate.
5
Enter details in AssetNode
In AssetNode Settings → Integrations, open the SSO / SAML card. Paste the IdP SSO URL, Entity ID and certificate, add at least one allowed email domain, switch Enable on and click Save.
หลังตั้งค่าเสร็จสิ้น
- Once SSO is active, giving new users access is done by assigning them in Okta.
- Enable "Force SSO" to require all users to sign in via Okta.